


Cybersecurity audit and vulnerability remediation for small and medium businesses: we check websites, servers, email and office IT, write a plain-language report, fix what we find and re-test, with written permission and an agreed scope before any test.
Discuss your projectTelegramWhatsApp
In short
- Audit of websites, servers, DNS and email security (SPF, DKIM, DMARC), access and backups.
- Pentest of web applications and the external perimeter only with the system owner's written permission.
- Incident response after a breach: cleanup, entry point closed, report.
- Remediation by our team: updates, configuration, MFA, backups with a verified restore.
- Preparation for ISO/IEC 27001 and CyberSecure Canada; fixed quote once the scope is agreed.
Cybersecurity services and what you get
- Website and server security audit. External perimeter, CMS and plugins, hosting panels, TLS and security headers, DNS and email (SPF, DKIM, DMARC), access controls and MFA, backups. You get a written report: what we found, how dangerous it is, what to fix today, this month and later, with a short version for the owner.
- Web application and perimeter pentest. Run only with written permission of the system owner, agreed targets and a time window, with the OWASP Top 10 as a baseline. You get reproducible findings with evidence, a remediation plan and a re-test of the fixes within the same scope.
- Incident response. We look for malicious code and webshells, find how attackers got in and what leaked, close the entry point and restore operations. You get a clean site or server, changed passwords and keys, a backup verified by a test restore and a report.
- Hardening and remediation. Updates, server configuration, permissions, MFA, backups with a verified restore, monitoring and alerts. You get a completed checklist.
- ISO/IEC 27001 and CyberSecure Canada preparation. Policies, risk register, Statement of Applicability, internal audit. You get the document package and a list of what is left before the certification audit.
How we use AI tools in security work
Our team uses its own experience and strong tooling, including Claude models, to find problems faster. Every finding is checked by a person before it reaches your report, and we fix what we find. Tools and AI models are used within their rules, and client data stays under the non-disclosure agreement.
How we work
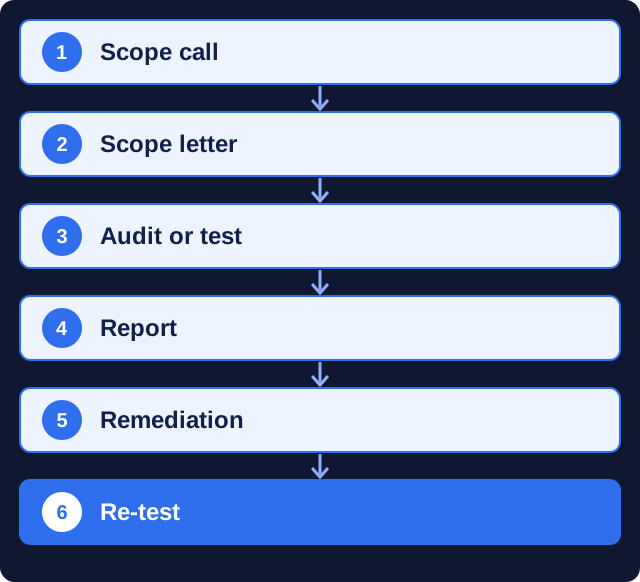
- Scope call. We agree what to check or fix.
- Scope letter. Written permission: targets, dates, exclusions.
- Audit or test. Checks within the agreed scope.
- Report. Plain-language summary and technical appendix.
- Remediation. Fixes by us or with your contractor.
- Re-test. We confirm the findings are closed.
How long does a security audit take?
The timeline is fixed in the scope letter and depends on the number of sites, servers and applications. Work starts after the letter is signed.
For an active incident we start as soon as we have access and permission, with the first goal of stopping the damage and preserving evidence. ISO/IEC 27001 preparation is planned in stages, based on the size of the company and the certification body's schedule.
What affects the cost of a security audit
We send a fixed quote once the scope is agreed. The main factors:
- number of websites, servers, applications and user accounts in scope;
- audit only, or audit with remediation;
- pentest depth and time window;
- incident urgency and the state of backups;
- documentation needed for ISO/IEC 27001.
What we need from you
- A list of systems to check and who owns them.
- Written permission from the owner of every system in scope.
- Access or a technical contact for each system.
- For incidents: what happened, when it was noticed and what has been changed since.
What you get and how we measure it
Every engagement ends with documents and a verified state:
- a report with findings rated by risk and a remediation plan;
- findings closed and confirmed by a re-test;
- MFA enabled, alerts configured and a restore from backup tested;
- for ISO/IEC 27001: a document package and a gap list before certification.
Why security work needs a contracted team
What we find most often at small and medium businesses:
- outdated CMS plugins and hosting panels open to known exploits;
- no SPF, DKIM or DMARC, so attackers send email in the company's name;
- backups that exist but have never been restored;
- shared admin passwords without MFA.
Working with a Kyiv team remotely
We work remotely with companies in the UK, the EU and North America: video calls, email, Telegram or WhatsApp, and shared documents for plans and reports. Kyiv is on UTC+2 (UTC+3 in summer), so our working day covers most of the UK and EU business day and the morning on the US East Coast. You get one project manager who is responsible for the timeline.
Why clients trust us
- A named legal entity. Cybersecurity work is performed by INNOVA CONSULT LTD., Corporation Number 1522612, Ottawa, Ontario (Corporations Canada).
- Verified for defensive AI use. INNOVA CONSULT LTD has been approved for Anthropic's Cyber Verification Program (CVP), which lets verified organisations use Claude models for defensive cybersecurity work.
- An ISMS we follow ourselves. We work according to our own information security management system based on ISO/IEC 27001:2022.
- Written scope before any test. Targets, dates, contacts and exclusions are fixed in a signed scope letter, and client data is covered by a non-disclosure agreement.
- Ten years of running websites. The Marketing MIX team has built and supported websites and servers for more than 10 years, so remediation is done by people who run such systems every day.
FAQ
What does a website security audit include?
External perimeter, CMS and plugins, hosting panels, TLS and headers, DNS and email security (SPF, DKIM, DMARC), access controls, MFA and backups, with a written report and remediation plan.
Do you run penetration tests?
Yes, only with written permission of the system owner and a signed scope letter that lists targets, dates and exclusions.
Our site was hacked. Can you help?
Yes. We remove malicious code, find and close the entry point, change passwords and keys, restore operations and give you a report of what happened.
Do you fix the vulnerabilities you find?
Yes. We fix them ourselves or together with your contractor, then re-test to confirm they are closed.
Can you prepare us for ISO/IEC 27001?
Yes: policies, risk register, Statement of Applicability and an internal audit, plus a list of what is left before the certification audit.
Who performs the work?
INNOVA CONSULT LTD., Corporation Number 1522612, Ottawa, Ontario, approved for Anthropic's Cyber Verification Program.
How much does a security audit cost?
We send a fixed quote once the scope is agreed. Describe what needs to be checked or fixed in the form.
Related services
- Penetration testing for websites and web apps
- Website hacked: clean-up and recovery
- ISO/IEC 27001 certification preparation
- Website support
- IT infrastructure for companies
- IT consulting
- Domain names and hosting
- Website redesign
Ready to start? Describe what needs to be checked or fixed in the form below. A manager replies with questions or a work plan and an estimate.


 DUNS Number: 68-606-2061
 NCAGE Number: A3G3J

 "INNOVA CONSULTING GROUP"


